
如何解决请求中的403个错误
如何解决请求中的403个错误
提问于 2018-05-23 10:41:59
我是春季启动休息服务的新手。我使用maven项目在spring引导中开发了一些rest。
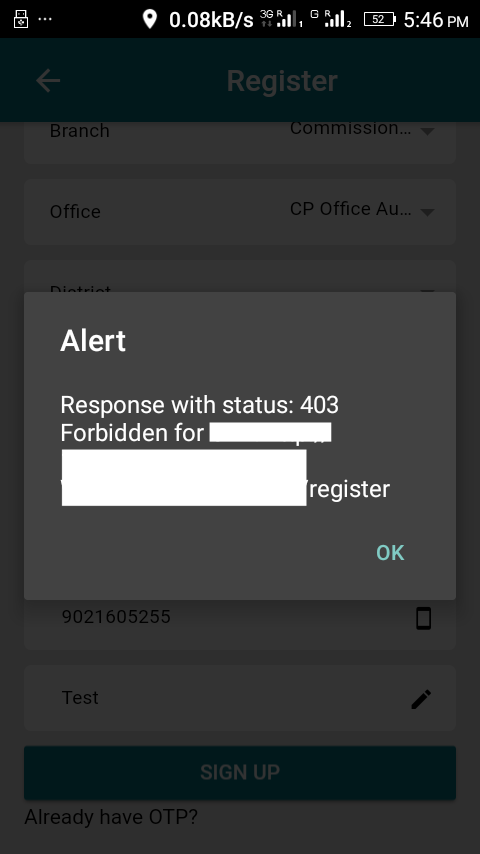
我已经成功地开发了Get和Post Api。我的GET方法在邮递员和手机上正常工作。当我试图从邮递员点击post方法时,它的工作正常,但是从手机上它给出了403个禁止的错误。
这是我的配置:
spring.datasource.url = jdbc:mysql://localhost/sampledb?useSSL=false
spring.datasource.username = te
spring.datasource.password = test
spring.jpa.properties.hibernate.dialect= org.hibernate.dialect.MySQL5InnoDBDialect
Hibernate ddl auto (create, create-drop, validate, update)
spring.jpa.hibernate.ddl-auto = update
请建议我如何解决错误。
回答 7
Stack Overflow用户
回答已采纳
发布于 2018-10-05 09:57:37
您必须禁用csrf保护,因为它在spring安全中默认启用:在这里,您可以看到允许cors起源的代码。
import org.springframework.context.annotation.Bean;
import org.springframework.security.config.annotation.web.builders.HttpSecurity;
import org.springframework.security.config.annotation.web.configuration.EnableWebSecurity;
import org.springframework.security.config.annotation.web.configuration.WebSecurityConfigurerAdapter;
import org.springframework.web.cors.CorsConfiguration;
import org.springframework.web.cors.CorsConfigurationSource;
import org.springframework.web.cors.UrlBasedCorsConfigurationSource;

@EnableWebSecurity
public class WebSecurityConfig extends WebSecurityConfigurerAdapter{

    @Override
    protected void configure(HttpSecurity http) throws Exception{
        http.cors().and().csrf().disable();
    }

    @Bean
    CorsConfigurationSource corsConfigurationSource() {
        CorsConfiguration configuration = new CorsConfiguration();
        configuration.setAllowedOrigins(Arrays.asList("*"));
        configuration.setAllowedMethods(Arrays.asList("*"));
        configuration.setAllowedHeaders(Arrays.asList("*"));
        configuration.setAllowCredentials(true);
        UrlBasedCorsConfigurationSource source = new UrlBasedCorsConfigurationSource();
        source.registerCorsConfiguration("/**", configuration);
        return source;
    }

}Stack Overflow用户
发布于 2021-07-06 13:22:55
在Spring安全性跨站点检查中,默认启用,我们需要通过创建一个单独的类来停止交叉检查来禁用它。
package com.baba.jaxws;

import org.springframework.context.annotation.Configuration;
import org.springframework.security.config.annotation.web.builders.HttpSecurity;
import org.springframework.security.config.annotation.web.configuration.WebSecurityConfigurerAdapter;

@Configuration
public class SecurityConfig extends WebSecurityConfigurerAdapter{

     @Override
    //we have stopped the csrf to make post method work
        protected void configure(HttpSecurity http) throws Exception{
            http.cors().and().csrf().disable();
        }
}Stack Overflow用户
发布于 2018-05-23 14:57:59
可能的原因:
- 来自邮递员的请求不同于移动请求(uri、方法、标头)。
- 无效令牌
- CORS (阅读一些关于它的内容,google充满了文章)在控制器中添加了@CrossOrigin注释。
- 移动应用程序在执行POST之前执行选项请求,而您则阻止选项请求。如果来自postman的选项请求也被阻止,则添加属性Spring.mvc.分派-options-request=true。此外,如果您正在使用spring安全性,则还必须显式地允许对它的选项请求。
页面原文内容由Stack Overflow提供。腾讯云小微IT领域专用引擎提供翻译支持
原文链接:
https://stackoverflow.com/questions/50486314
复制相关文章
相似问题
腾讯云开发者

Copyright © 2013 - 2026 Tencent Cloud. All Rights Reserved. 腾讯云 版权所有
深圳市腾讯计算机系统有限公司 ICP备案/许可证号:粤B2-20090059  粤公网安备44030502008569号
腾讯云计算(北京)有限责任公司 京ICP证150476号 | 京ICP备11018762号