
从时间戳服务器丢失时间戳的pdf签名
从时间戳服务器丢失时间戳的pdf签名
提问于 2020-01-21 16:54:25
我尝试使用外部web服务对pdf进行数字签名。此web服务包含用户证书,用户可以使用他们的凭据和一次生成的密码访问该证书。
Sidenote: web服务应该期望pdf摘要(散列),但奇怪的是它接受了整个文件。
无论如何,实现如下:
using iTextSharp.text.pdf;
using iTextSharp.text.pdf.security;

// OTP = One Time Password code
public void SignPdf(string username, string password, string otp)
{
    byte[] file = GetFileFromPath("D:\test.pdf");
    var fieldName = "signatureField";
    string tempFilePath = "D:\test1temp.pdf");

    using (var pdfReader = new PdfReader(file))
    {
        using (var signedPdf = new FileStream(tempFilePath, FileMode.Create))
        {
            using (var pdfStamper = PdfStamper.CreateSignature(pdfReader, signedPdf, '\0', null, true);
            {
                // Prepare signature
                PdfDate date = new PdfDate();
                var fullSignDate = date.GetW3CDate();
                var signDate = fullSignDate.Substring(0, fullSignDate.IndexOf("T"));
                var signTime = fullSignDate.Substring(fullSignDate.IndexOf("T") + 1);
                var signatureAppearance = pdfStamper.SignatureAppearance;
                signatureAppearance.SetVisibleSignature(fieldName);
                signatureAppearance.Layer2Text=($"Digitally signed by: Test User");

                // Get font
                signatureAppearance.SignatureRenderingMode = PdfSignatureAppearance.RenderingMode.DESCRIPTION;
                signatureAppearance.CryptoDictionary = GetPdfSignature(signatureAppearance);
                signatureAppearance.PreClose(new Dictionary<PdfName, int> { [PdfName.CONTENTS] = 8192 * 2 + 2 });

                // Get file content as base64 string
                var ms = new MemoryStream();
                signatureAppearance.GetRangeStream().CopyTo(ms);
                fileAsBase64 = ms.ToArray();

                // Sign hash (the "hash" is the whole document)
                signature = GetSignedHash(Convert.ToBase64String(fileAsBase64), username, password, otp);

                if (signature != null)
                {
                    EmbedSignatureToPdf(signatureAppearance, signatureWithTimeStamp);
                    success = true;
                }
            }
        }
    }
}

private static PdfDictionary GetPdfSignature(PdfSignatureAppearance sa)
{
    return new PdfSignature(PdfName.ADOBE_PPKLITE, PdfName.ADBE_PKCS7_DETACHED)
    {
        Reason = sa.Reason,
        Location = sa.Location,
        SignatureCreator = sa.SignatureCreator,
        Contact = sa.Contact,
        Date = new PdfDate(sa.SignDate)
    };
}

private byte[] GetSignedHash(string hash, string username, string password, string otp)
{
    // Call external web service and get a the signed hash
}

private void EmbedSignatureToPdf(PdfSignatureAppearance signatureAppearance, byte[] signature)
{
    var array = new byte[8192];
    Array.Copy(signature, 0, array, 0, signature.Length);
    var pdfDictionary = new PdfDictionary();
    pdfDictionary.Put(PdfName.CONTENTS, new PdfString(array).SetHexWriting(true));
    signatureAppearance.Close(pdfDictionary);
}
pdf已成功签名,但使用Adobe并检查签名字段,似乎缺少可信的时间戳,如图片中所示:
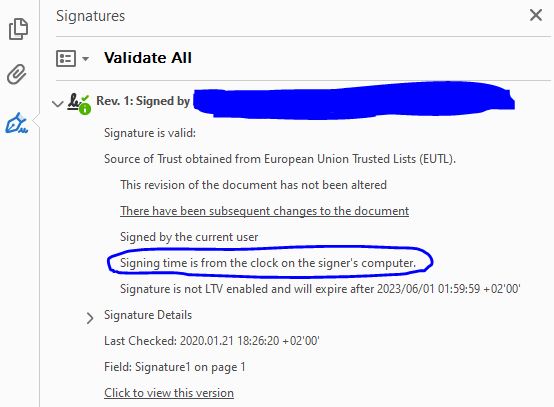
似乎来自远程服务的响应是一个签名对象,我只需将其嵌入到PDF文件中即可。
我的问题是:由于我收到的签名不包含来自时间戳服务器的时间戳,我可以在此时嵌入这样的时间戳吗?或者远程web服务应该在向我发送签名之前添加它吗?
谢谢!
回答 1
Stack Overflow用户
回答已采纳
发布于 2020-02-11 09:39:10
,因为我收到的签名不包含来自时间戳服务器的时间戳,我可以在此时嵌入这样的时间戳吗?或者远程web服务应该在向我发送签名之前添加它?
这样的时间戳作为无符号属性添加到签名容器中。由于没有签名,所以可以在应用签名后更改签名容器中的无符号属性,例如可以添加其他属性。
因此,您自己尤其可以将时间戳添加到从服务中检索的签名容器中。
但是,根据签名的性质,您可能需要增加在pdf中创建的占位符的大小,以便有足够的空间来创建额外的时间戳。
页面原文内容由Stack Overflow提供。腾讯云小微IT领域专用引擎提供翻译支持
原文链接:
https://stackoverflow.com/questions/59845795
复制相关文章
相似问题
腾讯云开发者

Copyright © 2013 - 2026 Tencent Cloud. All Rights Reserved. 腾讯云 版权所有
深圳市腾讯计算机系统有限公司 ICP备案/许可证号:粤B2-20090059  粤公网安备44030502008569号
腾讯云计算(北京)有限责任公司 京ICP证150476号 | 京ICP备11018762号