
如何在functions.php中正确创建自定义窗体的链接
我正在尝试在functions.php中创建自己的表单。我做了很多研究,发现使用Post /重定向/ Get来避免发布邮件请求是最安全的。一切都很好。表单发送POST,操作文件处理所有内容,将其保存到会话并重定向回。表单在页面上:http://plovarnaluhacovice.icreation.cz/my-account/zustatek-kreditu/
但我的问题是,出于安全考虑,我不希望链接“发送”有一个链接:http://plovarnaluhacovice.icreation.cz/wp-content/themes/Divi_Child/process.php,,但http://plovarnaluhacovice.icreation.cz/my-account/zustatek-kreditu/process.php。
为了使它变得有点复杂,我使用了WooCommerce插件,这个页面(/zustatek-kreditu/)被添加到WooCommerce "My Account“页面菜单(图)中。
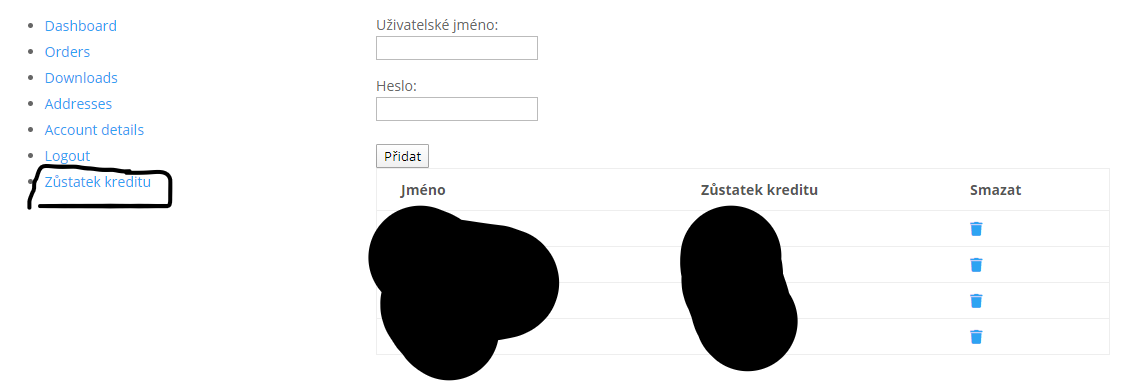
表格:
<form action="http://plovarnaluhacovice.icreation.cz/wp-content/themes/Divi_Child/process.php" method="post">
    <p>Uživatelské jméno: <br><input type="text" name="username" /></p>
    <p>Heslo: <br><input type="password" name="password" /></p>
    <br><button type="submit" name="save">Přidat</button>
</form>
文件结构:
wp-内容/主题/ 1. Divi_Child 2. functions.php 3. process.php
自定义WooCommerce菜单:
//ZŮSTATEK KREDITU

// ------------------

// 1. Register new endpoint to use for My Account page

// Note: Resave Permalinks or it will give 404 error


function zustatek_kreditu_endpoint() {
    add_rewrite_endpoint( 'zustatek-kreditu', EP_ROOT | EP_PAGES );
}

add_action( 'init', 'zustatek_kreditu_endpoint' );

// ------------------

// 2. Add new query var

function zustatek_kreditu_query_vars( $vars ) {
    $vars[] = 'zustatek-kreditu';
    return $vars;
}

add_filter( 'query_vars', 'zustatek_kreditu_query_vars', 0 );

// ------------------

// 3. Insert the new endpoint into the My Account menu

function zustatek_kreditu_link_my_account( $items ) {
    $items['zustatek-kreditu'] = 'Zůstatek kreditu';
    return $items;
}

add_filter( 'woocommerce_account_menu_items', 'zustatek_kreditu_link_my_account' );

// ------------------

// 4. Add content to the new endpoint

?>
    <form action="http://plovarnaluhacovice.icreation.cz/wp-content/themes/Divi_Child/process.php" method="post">
        <p>Uživatelské jméno: <br><input type="text" name="username" /></p>
        <p>Heslo: <br><input type="password" name="password" /></p>
        <br><button type="submit" name="save">Přidat</button>
    </form>
<?php

add_action( 'woocommerce_account_zustatek-kreditu_endpoint', 'hlavniMetoda' );
process.php文件:
<?php

require_once __DIR__ . '/../../../wp-config.php';
global $wp;
global $wpdb;
$current_user_id = wp_get_current_user()->ID;

if (isset($_POST['save'])) {
    if($current_user_id > 0) {
        $username = $_POST['username'];
        $password = $_POST['password'];

        $dotaz = "INSERT INTO {$wpdb->prefix}abonent(username, password, ID_users) VALUES('{$username}', '{$password}', {$current_user_id})";
        $result = $wpdb->query($dotaz);

        if($result) {
            $_SESSION['zprava'] = "Přidáno";
        }
        else {
            $_SESSION['zprava'] = "Chyba.";
        }
    }
    header("Location: http://plovarnaluhacovice.icreation.cz/muj-ucet/zustatek-kreditu");
}
?>回答 1
Stack Overflow用户
发布于 2020-02-15 13:40:12
- 最简单的解决方案是在wp中创建一个页面模板,将其添加到您的主题文件夹中,名为" page - process.php“,并将process.php的所有代码放入该模板中,并将以下文本添加到该模板的顶部:
- 创建一个wp页面,并在其上选择此模板作为“页面属性”元框下的页面模板。表单代码中的
- 将操作URL替换为您刚刚创建的页面并链接到您创建的新页面模板。
action="http://plovarnaluhacovice.icreation.cz/wp-content/themes/Divi_Child/process.php"
Recap:,您要将"porcess.php“替换为WordPress上的普通页面,该页面将使用放置在"process.php”上的页面PHP代码,但此特权将允许您在wp页面上运行代码,而不是直接在主题PHP文件上运行。
谢谢,让我知道发生了什么!)
https://stackoverflow.com/questions/60238927
复制相似问题
腾讯云开发者

Copyright © 2013 - 2026 Tencent Cloud. All Rights Reserved. 腾讯云 版权所有
深圳市腾讯计算机系统有限公司 ICP备案/许可证号:粤B2-20090059  粤公网安备44030502008569号
腾讯云计算(北京)有限责任公司 京ICP证150476号 | 京ICP备11018762号