
Java /TLS(没有可用的身份验证方案)
Java /TLS(没有可用的身份验证方案)
提问于 2021-07-07 10:26:54
你好,因为我用我的KeyStore修复了我的最后一个问题,KeyTool有一个问题,我想问另一个问题。
现在,我将我的“让我们加密证书”导入到我的KeyStore中,但在客户端开始连接时得到以下消息
没有可用的身份验证方案
我尝试了很多东西,在这里读了很多关于Stackoverflow的文章,但是我没有结束。
下面是Stacktrace:
javax.net.ssl.SSLHandshakeException: No available authentication scheme
    at sun.security.ssl.Alert.createSSLException(Alert.java:131)
    at sun.security.ssl.Alert.createSSLException(Alert.java:117)
    at sun.security.ssl.TransportContext.fatal(TransportContext.java:357)
    at sun.security.ssl.TransportContext.fatal(TransportContext.java:313)
    at sun.security.ssl.TransportContext.fatal(TransportContext.java:304)
    at sun.security.ssl.CertificateMessage$T13CertificateProducer.onProduceCertificate(CertificateMessage.java:970)
    at sun.security.ssl.CertificateMessage$T13CertificateProducer.produce(CertificateMessage.java:959)
    at sun.security.ssl.SSLHandshake.produce(SSLHandshake.java:420)
    at sun.security.ssl.ClientHello$T13ClientHelloConsumer.goServerHello(ClientHello.java:1096)
    at sun.security.ssl.ClientHello$T13ClientHelloConsumer.consume(ClientHello.java:1032)
    at sun.security.ssl.ClientHello$ClientHelloConsumer.onClientHello(ClientHello.java:716)
    at sun.security.ssl.ClientHello$ClientHelloConsumer.consume(ClientHello.java:683)
    at sun.security.ssl.SSLHandshake.consume(SSLHandshake.java:376)
    at sun.security.ssl.HandshakeContext.dispatch(HandshakeContext.java:479)
    at sun.security.ssl.HandshakeContext.dispatch(HandshakeContext.java:457)
    at sun.security.ssl.TransportContext.dispatch(TransportContext.java:200)
    at sun.security.ssl.SSLTransport.decode(SSLTransport.java:154)
    at sun.security.ssl.SSLSocketImpl.decode(SSLSocketImpl.java:1290)
    at sun.security.ssl.SSLSocketImpl.readHandshakeRecord(SSLSocketImpl.java:1199)
    at sun.security.ssl.SSLSocketImpl.startHandshake(SSLSocketImpl.java:401)
    at sun.security.ssl.SSLSocketImpl.startHandshake(SSLSocketImpl.java:373)
    at de.bytestore.mytriox.network.server.ServerSocket$1.run(ServerSocket.java:204)
    at java.lang.Thread.run(Thread.java:748)
这是我的KeyStore文件:
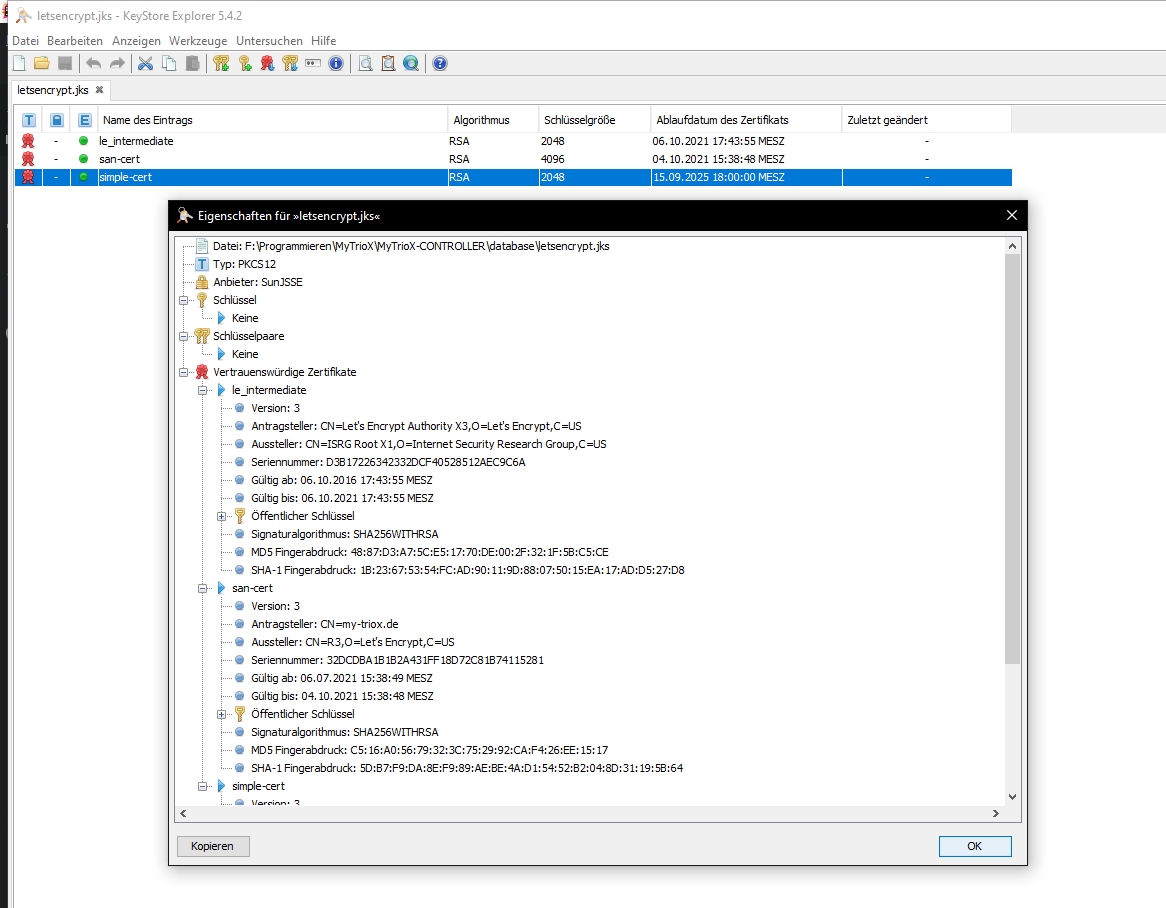
我是否需要为SecureSocket选择一个别名,还是你有其他的想法?
向简问好
回答 1
Stack Overflow用户
发布于 2022-09-15 16:05:39
我在Spring云网关服务中也看到了同样的错误。原因是我在中创建了一个密钥存储和密钥别名,没有密码。所以,当我修改application.yaml时
server:
  port: 8182
  ssl:
    enabled: true
    key-store: classpath:gateway-key-store.p12
    key-store-password:  <-empty
    key-alias: gateway-key
    key-password:  <-empty
例外消失了。
页面原文内容由Stack Overflow提供。腾讯云小微IT领域专用引擎提供翻译支持
原文链接:
https://stackoverflow.com/questions/68284274
复制相关文章
相似问题
腾讯云开发者

Copyright © 2013 - 2026 Tencent Cloud. All Rights Reserved. 腾讯云 版权所有
深圳市腾讯计算机系统有限公司 ICP备案/许可证号:粤B2-20090059  粤公网安备44030502008569号
腾讯云计算(北京)有限责任公司 京ICP证150476号 | 京ICP备11018762号