
Azure devOps部署发行版设置
Azure devOps部署发行版设置
提问于 2022-10-28 11:46:59
如果连接字符串是作为释放管道中的一个秘密变量设置的。
是否有任何方式或任何人查看秘密变量?如果是的话,我们怎么做呢?
回答 1
Stack Overflow用户
发布于 2022-10-31 02:38:09
我在YAML文件中为您编写了一个powershell演示(基于Daniel的想法),请注意,在管道上,您将无法输出值,因为所有相同的值都将被管道捕获,并且所有这些值都将被“*”覆盖。
trigger:
- none

pool:
  vmImage: ubuntu-latest

steps:
- task: PowerShell@2
  inputs:
    targetType: 'inline'
    script: |
      Write-Host $(not_secure)
      Write-Host $(secure)

      #convert string to based64 string:

      $secret = "$(secure)"

      $secret = [System.Convert]::ToBase64String([System.Text.Encoding]::UTF8.GetBytes($secret))

      Write-Host $secret

Write-Host "value2" #Whenever the pipeline capture the same value of the secured secret, the pipeline will output '***'. So doing any tricks inside the pipeline can't make the pipeline output this value每当管道捕获相同值的安全秘密时,管道将输出`'*'`**.
。因此,在管道中执行任何操作都不能使管道输出这个值。
我的管线输出:
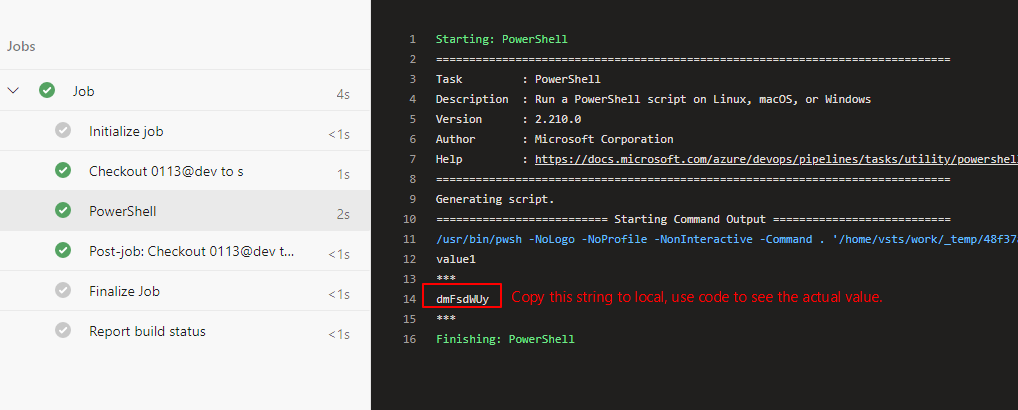
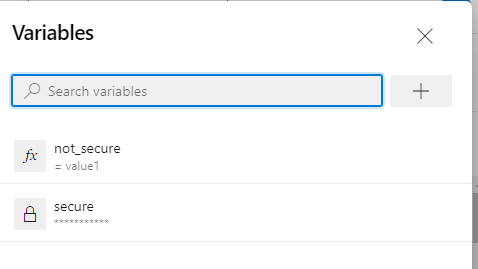
我的变量:
get_secret_of_pipeline.ps1(run这个在你的机器上。)
$secret = "dmFsdWUy"

$secret = [System.Text.Encoding]::UTF8.GetString([System.Convert]::FromBase64String($secret))

Write-Host $secret
成功地获得秘密的价值:

页面原文内容由Stack Overflow提供。腾讯云小微IT领域专用引擎提供翻译支持
原文链接:
https://stackoverflow.com/questions/74234940
复制相关文章
相似问题
腾讯云开发者

Copyright © 2013 - 2026 Tencent Cloud. All Rights Reserved. 腾讯云 版权所有
深圳市腾讯计算机系统有限公司 ICP备案/许可证号:粤B2-20090059  粤公网安备44030502008569号
腾讯云计算(北京)有限责任公司 京ICP证150476号 | 京ICP备11018762号